
Business Risk Assessment
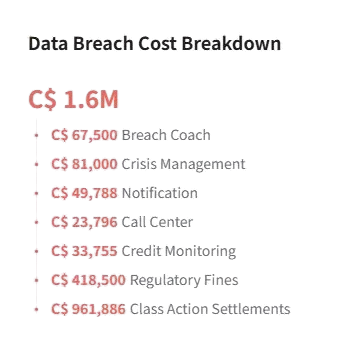
Most business owners find out what a cyber attack would cost them the day it happens. Find out first, and walk away with a clear plan.
You can’t manage a risk you can’t see
You’ve got antivirus. You’ve got backups, probably. Your IT provider says everything’s fine.
But nobody has ever shown you, in plain language, where your business is actually exposed, what it would cost you if someone got in, and what to fix first. That’s what our business risk assessment does. In 30 days, you’ll know exactly where you stand.
What we usually find
We’ve run this assessment many times, and the same three things keep showing up.
In most of our phishing tests, more than 70% of staff clicked a link or opened an email they shouldn’t have. Good people, busy day, convincing email.
Staff passwords shorter than six characters. Found again and again, in organizations that thought they had a password policy.
Email addresses and passwords already sitting on the dark web. Most owners have no idea until we show them.
None of these are exotic. All of them are fixable. But you have to see them first.
How it works
- A short introductory call to understand your business.
- A discovery call with your decision makers, so we can tie the findings to what matters to you.
- Lightweight assessment software runs in the background for 14 to 30 days.
- A one-hour results meeting with your leadership team: everything we found, what it means, and what needs to be done first.
A second opinion on your current IT
Some clients come to us because they’re not sure what they’re getting for their IT spend.
The assessment answers that. We don’t knock other providers.
We show you the evidence and let you decide whether it matches what you’ve been told.
Sometimes the answer is that your provider is doing a solid job. Either way, you’ll know.
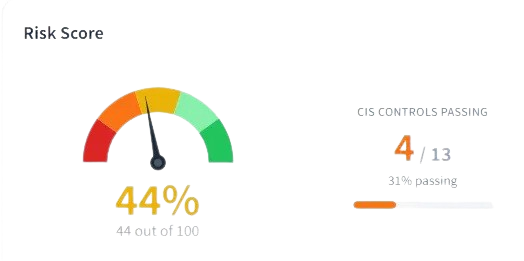
Here’s what you’ll know when we’re done
Computers and accounts
Which computers and accounts are out of date or set up wrong.
Microsoft 365 or Google Workspace
Whether every account is protected by multi-factor authentication, and how your security settings compare with best practices.
Your domain
Whether your domain can be abused to impersonate your business.
The dark web
Which staff email addresses and passwords have already leaked.
Sensitive data
Whether information like SINs or card numbers is stored where it shouldn’t be.
AI and staff awareness
Which AI tools your staff use, what data goes into them, and in the full assessment, how your team handles a phishing email.
$1,500
For organizations with up to 10 users or devices, whichever is greater. Larger organizations receive a quote. Penetration testing is available as an add-on. We’re not the cheapest. We work on value, and this assessment is where you find out what that means.
What you keep
A detailed written report covering every finding, in plain language, that you keep whether or not you ever work with us again. Your findings are confidential. It shows you where the problems are and what needs to be done. Whether you have us do the work or take it to your current provider is your call.
Business phone systems: common questions
How long does a business risk assessment take?
14 to 30 days. Usually 30; we can do it in 14 when timing matters.
What does it cost?
$1,500 for up to 10 users or devices, whichever is greater. Larger organizations receive a quote.
Do we have to sign up for managed services afterwards?
No. You keep the report either way.
Can you check whether our current IT provider is doing a good job?
Yes. That’s one of the most common reasons businesses book this.
Do you include a phishing test?
Yes, in the full assessment, when account access allows.
Is our information confidential?
Yes. Your findings and report are kept confidential.